On air · 1 of 3 networks
Pentest-Tools.com
- pentest-tools.com
- RO
- 66 employees
Pentest-Tools.com’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 24. Watch Pentest-Tools.com with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 14 | Checked 29 Oct 2026 | See all 24 ads → | ||
| Meta | Not checked | — | |||
| Recently | 100+ | Ads on the Google Ads Transparency Center | Checked 6 Oct 2026 | Collect them with the API → |
Pentest-Tools.com has 14 live LinkedIn ads. We recorded 100+ Google ads on 6 Oct 2026.
Latest ads
- LINKEDIN · EVENTSince 28 Jul 2026
An AI tool found 300 issues in a pentest. 250 of them were junk. That's a direct quote from our new survey of 158 security practitioners on how AI is actually changing #pentesting. Next Wednesday, Jan Pedersen and Robert Tănase, our Lead Product Manager, are breaking down which results surprised us most during Office Hours: 📥 the triage tax (AI found more, proving it got harder) 🚩 the trust problem (why one fabricated finding costs more than a missed one) 🛠️ what we built in response. 30 minutes live. 15 minutes of open Q&A. One session. Wednesday, July 29 8:00 AM Los Angeles 11:00 AM New York 4:00 PM London 6:00 PM Bucharest Register at the link in the comments. 👇👇👇 #penetrationtesting #offensivesecurity #cybersecurity
- LINKEDIN · IMAGESince 18 Jul 2026
#WordPress admins - we got you covered! 🫡 → We've just shipped detection for #wp2shell through our Network Scanner. ⚡️ The fastest way to use it is to: ◉ run a single-CVE scan for CVE-2026-63030 - which also covers CVE-2026-60137 - the SQL injection flaw that chains to give attackers RCE ◉ Based on your scan results, either patch or confirm you're already on 6.8.6, 6.9.5, or 7.0.2. ◉ Re-scan to confirm remediation and rule out residual exposure across your other assets. Remember: updating your main install doesn't cover *every* WP instance you own. Using Pentest-Tools.com means you can expand visibility across your wider attack surface, not just the site you remember exists. Technical CVE details below. ↘︎↘︎↘︎ #vulnerabilityassessment #ethicalhacking #offensivesecurity
- LINKEDIN · EVENTSince 13 Jul 2026
React2Shell. NGINX Rift. cPanel. ToolShell. Every one of them was a scramble for someone. Which assets does this touch? Is it real? Did we actually close it? Next week, on Wednesday, Pentest-Tools.com Office Hours is about turning that scramble into a workflow. Jan Pedersen hosts a live walkthrough of emergency CVE response, across two situations: an environment you’ve just inherited and don’t fully know, and one you know well and want reacting to new CVEs for you. How to find affected assets fast, how to tell a genuine exposure from a version match, and how comparing one scan to the next proves what you actually closed. 30 minutes live. 15 minutes of open Q&A. One session. Register at the link in the comments. 👇👇👇 #penetrationtesting #offensivesecurity #cybersecurity
- LINKEDIN · IMAGESince 8 Jun 2026
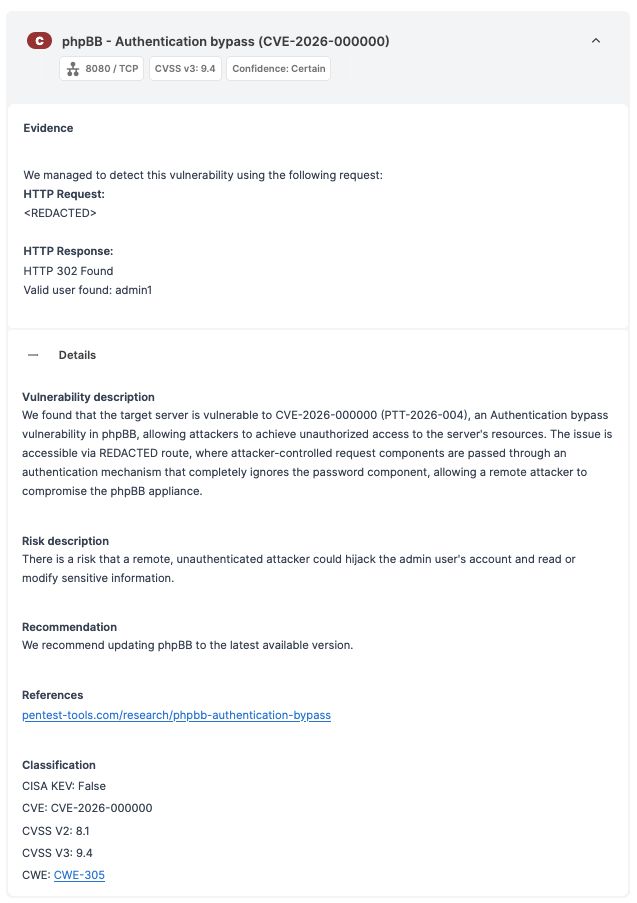
🏴☠️ New #offensivesecurity research: phpBB authentication bypass discovered by Pentest-Tools.com! And it packs *two* vulnerabilities. 👇👇👇 ⚡PTT-2026-004 (CVSS 9.4 - critical): one HTTP request, a target username, a wrong password phpBB never checks. You get back a valid session cookie for that account. Admins included. Works on every default phpBB install up to and including 3.3.16, no prior access needed. The vulnerable code path got introduced more than 10 years ago and survived multiple major releases and security reviews before Alex Dan, offsec researcher at Pentest-Tools.com, found it along with... ⚡PTT-2026-005 (CVSS 8.3 - high) which chains two OAuth defects for a silent account takeover on sites with OAuth configured. In some cases, the victim doesn't need to click anything - an image tag embedded in a forum post is enough to trigger it. ⬇️⬇️⬇️ Full technical breakdown & mitigation steps in the comment below! #penetrationtesting #ethicalhacking #infosec
- LINKEDIN · IMAGESince 20 May 2026
🚨 Worried about your #NGINX web servers? 👉We built a *free* scanner for CVE-2026-42945 (NGINX Rift). 👇 Check your targets now (no account required): https://lnkd.in/e8WhaTVY Once the scan completes (and if your target is vulnerable), you'll get a finding that includes: ✅ the detected NGINX version ✅the vulnerable range it falls into ✅the CVSS score & severity rating ✅remediation guidance Download it as a PDF and share it with whoever handles remediation. Oh, and one thing to check before you call it patched: upgrading your primary NGINX install *doesn’t* cover copies embedded in container images or Kubernetes ingress controllers. Those need separate inventory and patching. PS: We also have a dedicated Kubernetes vulnerability scanner. You can find it on our website. #offensivesecurity #pentesting #vulnerabilitymanagement
- LINKEDIN · EVENTSince 21 Apr 2026
This Wednesday, April 22, Jan Pedersen kicks off our weekly Office Hours with a live walkthrough of how to run Pentest-Tools.com as a continuous compliance layer. Scheduled scans that build the evidence trail for you. Before-and-after remediation proof. Reports that work for both the SOC and the auditor. 30 minutes live. 15 minutes of open Q&A. Two sessions, same day. Pick the one that fits your timezone. Links in the comments section 👇
6 of 24 adsSign up to see every Pentest-Tools.com ad, filter by format and date, and get alerts on new ones.
See all 24 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.