Not on air · 2 of 3 networks checked
Pembroke Privacy
- pembrokeprivacy.com
- IE
- 19 employees
Pembroke Privacy’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 28. Watch Pembroke Privacy with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 29 Oct 2026 | See all 28 ads → | ||
| Meta | Not checked | — | |||
| Recently | 33 | Ads on the Google Ads Transparency Center | Checked 6 Oct 2026 | Collect them with the API → |
Pembroke Privacy has no live LinkedIn ads. We recorded 33 Google ads on 6 Oct 2026.
Latest ads
- LINKEDIN · EVENTSince 17 Oct 2026
Join Pembroke Privacy on 28 October at 11am IST for our LinkedIn Live, Part 1: How to create a compliant ROPA. We’ll cover what a RoPA is, which organisations need one, what it should look like and the information it must include. We’ll also explore how to create a RoPA for your organisation and when to review it.
- LINKEDIN · IMAGESince 16 Oct 2026
Professional privacy credentials still matter, especially when the work gets more complex. Not because the letters themselves do the job, but because strong certification routes help build the knowledge, judgment and confidence the work actually demands. As privacy, governance and AI obligations become more layered, organisations need people who can move beyond surface-level awareness. People who understand the principles, the operational realities and the risk decisions underneath them. That is where professional training earns real credibility. Whether someone is building a career in privacy or an organisation is strengthening its internal capability, recognised programmes like CIPP/E, CIPM, CIPT and AIGP still carry weight for a reason. Pembroke Privacy offers IAPP training options designed to support professionals and organisations looking to build stronger privacy and AI governance capability. https://lnkd.in/esPziUQ #PrivacyTraining #IAPP #CIPPE #CIPM #CIPT #AIGP #DataProtection
- LINKEDIN · IMAGESince 16 Oct 2026
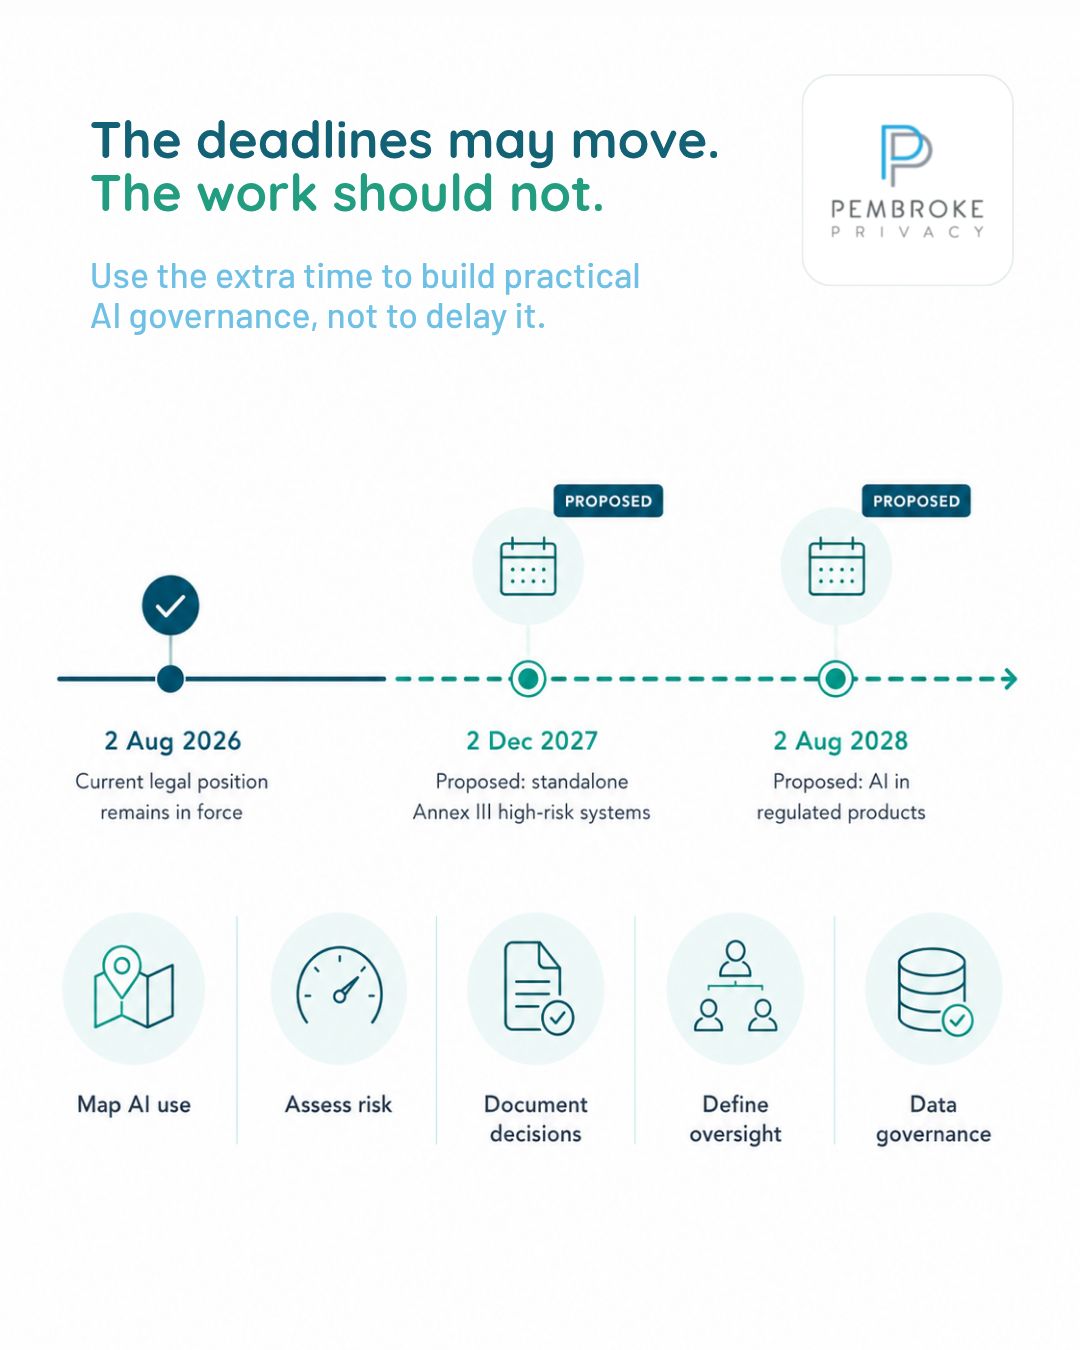
The AI Act may be buying organisations time. It is not giving them permission to stand still. Recent EU developments suggest that certain high-risk AI compliance deadlines may move later, with proposed dates of 2 December 2027 for standalone Annex III high-risk systems and 2 August 2028 for AI embedded in regulated products. That sounds like breathing room. But breathing room is only useful if organisations use it well. The substance of AI governance has not disappeared. Organisations will still need to understand where AI is being used, assess risk, document decisions, define oversight, manage data governance, and build processes that can stand up to scrutiny. There is also an important caveat: until the final text is adopted, the original 2 August 2026 deadline remains legally in force. So the practical message is simple. Use the extra time to prepare, not to delay. Strong AI governance is not a last-minute compliance exercise. It is the structure that helps organisations make better decisions while the regulatory detail continues to settle. Pembroke Privacy supports organisations with AI governance services designed to make AI Act readiness more practical, structured and manageable. https://lnkd.in/eFx7YBUU #AIGovernance #EUAIAct #RiskManagement #Compliance #ResponsibleAI
- LINKEDIN · IMAGESince 16 Oct 2026
Board members do not need more noise. They need clearer visibility on risk. Privacy and AI governance issues rarely stay neatly inside legal or compliance teams. When something goes wrong, the consequences tend to reach reputation, trust, operations and leadership accountability very quickly. That is why board-level understanding matters. Not so directors can become technical specialists, but so they can ask better questions, recognise where oversight is thin, and understand the difference between a policy that exists and a governance model that actually works. Strong board training creates better visibility, better challenge and better decision-making. Pembroke Privacy provides training for board members designed to help leadership teams better understand data protection responsibilities and governance risk. https://lnkd.in/e6e4ymkM #BoardTraining #Governance #DataProtection #RiskManagement #Leadership
- LINKEDIN · IMAGESince 16 Oct 2026
Compliance gap assessments are about clarity. Most organisations do not need another vague sense that something might be missing. They need a clearer view of where the actual risks sit, which issues need urgent attention, and which improvements can be handled in a more measured way. That is what makes a gap assessment useful. It turns uncertainty into a working picture. Not a box-ticking exercise. Just a more grounded understanding of what is in place, what is weak, and what needs to change. That kind of clarity helps leadership prioritise properly and gives compliance work a firmer footing. Pembroke Privacy supports organisations with data protection gap assessments designed to identify compliance gaps and practical areas for improvement. https://lnkd.in/dfWipx2W #Compliance #GDPR #DataProtection #RiskAssessment #Governance
- LINKEDIN · IMAGESince 16 Oct 2026
An overflowing confidential waste bin is a data protection issue, not just a housekeeping problem. The Irish Data Protection Commission’s recent decision concerning an Irish healthcare system is a reminder that protecting personal data means looking beyond digital systems. Organised paper records can fall within the GDPR too. How they are stored, accessed, moved and disposed of deserves the same disciplined attention as information held electronically. For DPOs and operational teams, the practical questions are straightforward: • Who can access physical records, and where are they kept? • Are confidential waste arrangements effective in day-to-day use? • Do risk assessments reflect how staff actually handle documents? • Are the safeguards identified in DPIAs implemented and regularly reviewed? In this case the DPC issued a reprimand and required that relevant DPIAs be finalised and measures implemented within a fixed deadline. The lesson extends beyond healthcare: written policies need to be supported by effective controls in practice. In our latest article, Luisa Maciel Perez examines the decision and what it means for the management of physical records. Read the full article: https://lnkd.in/dyzzHrYf #DataProtection #GDPR #PrivacyGovernance
6 of 28 adsSign up to see every Pembroke Privacy ad, filter by format and date, and get alerts on new ones.
See all 28 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.