Not on air · 2 of 3 networks checked
Nudge Security
- nudgesecurity.com
- Computer and Network Security
- US
- 53 employees
Nudge Security’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 419. Watch Nudge Security with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 3 Nov 2026 | See all 419 ads → | ||
| Meta | Not checked | — | |||
| Recently | 100+ | Ads on the Google Ads Transparency Center | Checked 6 Oct 2026 | Collect them with the API → |
Nudge Security has no live LinkedIn ads. We recorded 100+ Google ads on 6 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 17 Jul 2026
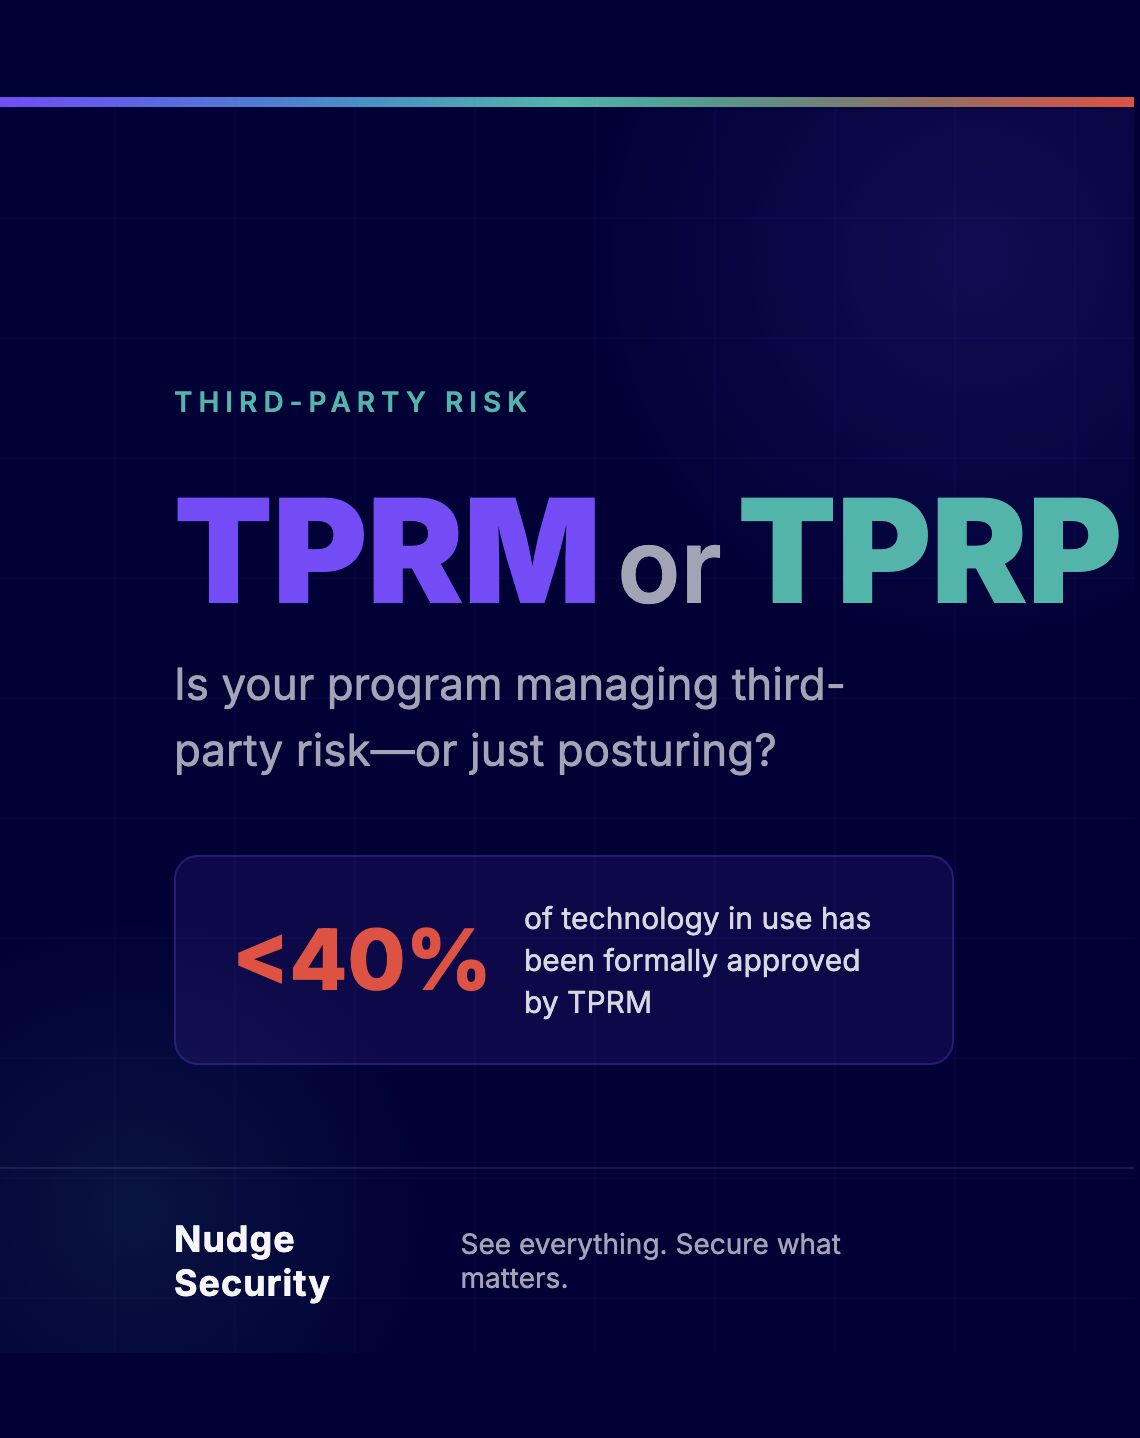
TPRM or TPRP? Here's a number that should make every security leader uncomfortable: less than 40% of the technology your employees actually use has been formally approved by a third-party risk management process. Read that again. Your TPRM program was built for a world where IT bought software through procurement. That world doesn't exist anymore. Employees sign up for SaaS tools and AI apps on their own—and the scope of how they use them changes constantly. The app you approved for one team's narrow use case is now integrated across your entire environment. So let's be honest—is your program actually managing third-party risk? Or is it just third-party risk posturing? The gap between what's approved and what's actually happening is where your real risk lives. Nudge Security gives you visibility into all the SaaS and AI your employees are using—in less than 24 hours—and shows you exactly how it's integrated into your environment. Stop posturing. Start seeing. 👇 #SaaS #TPRM #Cybersecurity #ShadowIT
- LINKEDIN · IMAGESince 17 Jul 2026
If I were a CISO trying to secure a modern, fast-moving, SaaS-heavy organization, this is the exact nightmare I’d be living: I’m responsible for data inside tools I didn’t approve, used by people I didn’t train, from devices I don’t control, in workflows I can’t see. That’s actually what security leaders keep telling me. And the root cause is simple: every employee has become their own CIO. Not because they’re careless - but because a $100/month SaaS tool can cut a week of work down to an hour. Of course they’re going to use it. The result? Productivity soars Visibility vanishes Security is left holding the risk. We’re not going back to centralized control. We built Nudge Security for this reality. Deploy in 5 minutes. No agents. No network changes. Instantly see every SaaS account ever created, and new ones as they are introduced. And, instead of blocking productivity, we intervene and engage employees to make governance collaborative, not combative. Centralized oversight. Decentralized action. Security that keeps up with your workforce. If you’ve ever wondered how much SaaS your org is really using… I’d be happy to show you. It’s always an eye-opener. See how you can get started today: https://lnkd.in/ecZciciY
- LINKEDIN · IMAGESince 17 Jul 2026
I've had at least a dozen CISOs tell me in the past month that AI governance feels like trying to childproof a house while the kids are already running around with scissors. Here's what's actually happening right now: - Your product team is using Claude to analyze customer data from Zendesk. - Your sales team is feeding Gemini prospect data from Salesforce. - Your engineering team has connected Cursor to your entire GitHub organization. The old playbook was: 👉 Assess the risk, build the policy, enable the technology. The new reality facing security teams in 2026: 👉 The tech is already enabled, the risk is already present and you're racing to just get visibility. What I find fascinating is that this isn't really an AI problem - it's a human behavior problem that AI has just made impossible to ignore. Every employee has always had the ability to make technology decisions that create security and governance challenges. AI just happens to move faster and touch more sensitive data than technologies of the past. It now spans MCP servers, agentic AI, and SaaS apps with AI features, as well as employees chatting and sharing corporate data with LLMs. If you're a security leader trying to figure out how to scale AI security governance at the pace of actual AI use, let’s talk. And, if you need hard data to prove what’s actually happening when it comes to AI use in your org, start with Nudge Security for a free shadow AI inventory.
- LINKEDIN · IMAGESince 17 Jul 2026
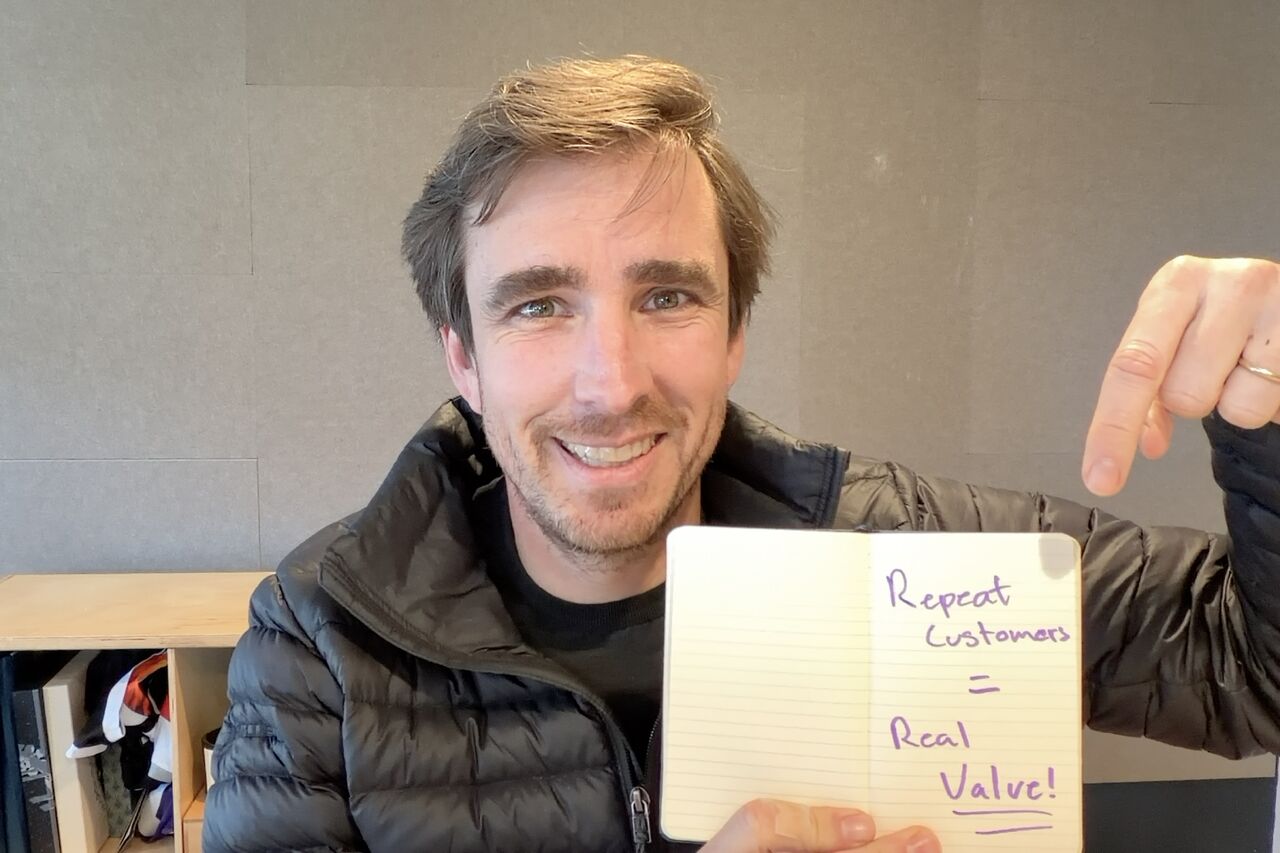
This news made my day: TWO of our newest customers are actually repeat purchasers. The security leader championing the deal had already used Nudge Security at their previous company. They literally brought us with them to their new role. This might be my favorite validation that we're solving real problems. Because here's the thing about security tools: nobody gets emotionally attached to them. You don’t bring them with you because you think the UI is pretty (although I would argue that ours very much is). Either they solve a problem for you or they quickly become shelfware. It’s that simple. When a security leader lands at a new organization and one of their first moves is to bring in the same platform they used before? That tells you something about the pain they're experiencing and the confidence they have in the solution. What these leaders tell me is consistent: "I knew I'd be walking into the same visibility gap. I knew my new team would be dealing with the same unmanaged SaaS sprawl. Why would I waste six months evaluating alternatives when I already know what works?" It's the ultimate product-market fit signal - not just that someone bought your product once, but that they found it valuable enough to champion it again in a completely different organization with different priorities, different budgets, and different stakeholders to convince. The best part? Nudge Security provides value from DAY ONE, no long complicated deployment to suffer through before you get to the fun stuff. If you’re ready to see what these security leaders already know, start your own free trial here: https://lnkd.in/dtEgckDS
- LINKEDIN · IMAGESince 6 Apr 2026
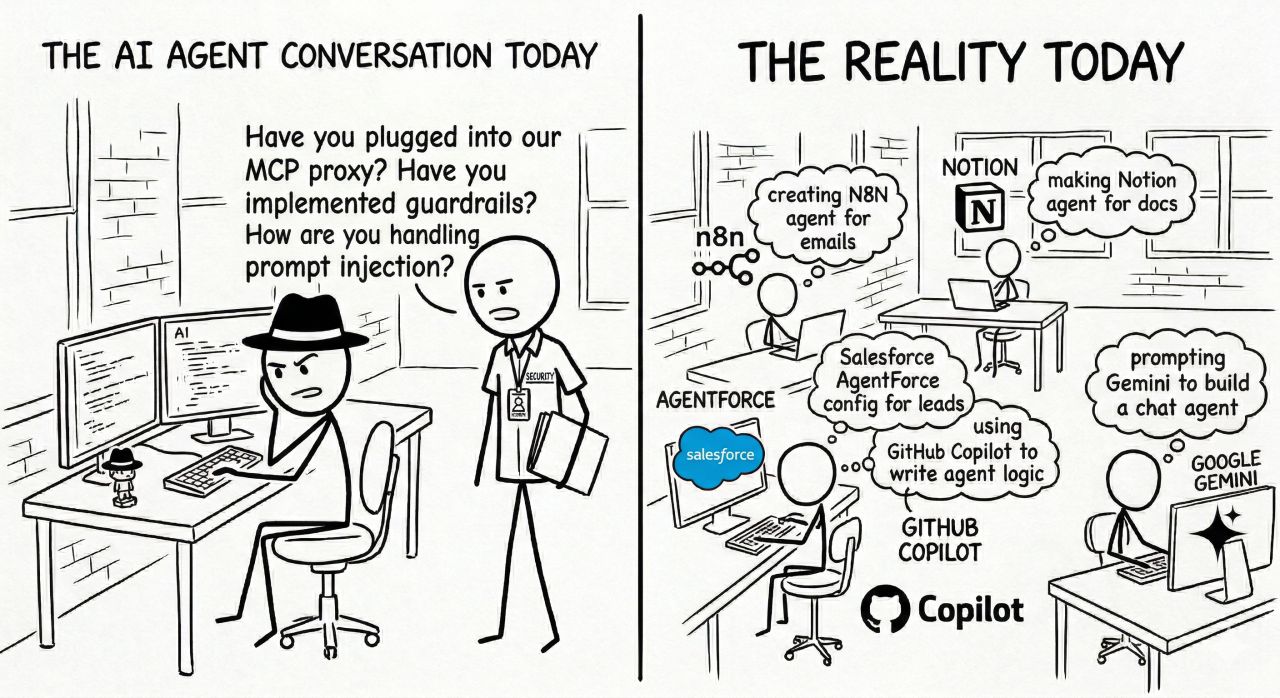
The AI agent security conversation has a blind spot. Everyone's focused on helping developers build secure agents. SDKs, frameworks, guardrails baked into code. That's important work. But here's what's actually happening on the ground: your marketing team just built an AI agent in Zapier. Your sales ops team wired one up in n8n. Someone in finance connected Copilot to a shared inbox. And a RevOps analyst spun up an Agentforce flow that touches live customer data. None of them wrote a line of code. None of them went through a security review. AI agents aren't a developer story anymore. They're a business user story. The same platforms that democratized automation—Zapier, n8n, Agentforce, Copilot—are now democratizing agent creation. And they're doing it without security teams in the loop. The question isn't "how do we help developers build agents securely?" It's "how do we help everyone build agents securely?" Because the next wave of AI risk won't come from a GitHub repo. It'll come from a no-code workflow that quietly connects an LLM to your production data—built by someone who's never heard of prompt injection. Security has to follow the agents. Wherever they're being built. #AIAgents #SaaSSecurity #ShadowAI #AIGovernance
- LINKEDIN · IMAGESince 26 Mar 2026
You can't secure what you can't see. Find shadow AI today, including apps, users, and risky integrations. Get a free shadow AI inventory.
6 of 419 adsSign up to see every Nudge Security ad, filter by format and date, and get alerts on new ones.
See all 419 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.