On air · 1 of 3 networks
Nightfall AI
- nightfall.ai
- US
- 131 employees
Nightfall AI’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 229. Watch Nightfall AI with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 163 | Checked 31 Oct 2026 | See all 229 ads → | ||
| Meta | None recorded | 0 | No active ads recorded on the Meta Ad Library | Checked 24 Oct 2026 | Collect them with the API → |
| Recently | 33 | Ads on the Google Ads Transparency Center | Checked 5 Oct 2026 | Collect them with the API → |
Nightfall AI has 163 live LinkedIn ads. Its Facebook page had no active ads on 24 Oct 2026, and we recorded 33 Google ads on 5 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 26 Oct 2026
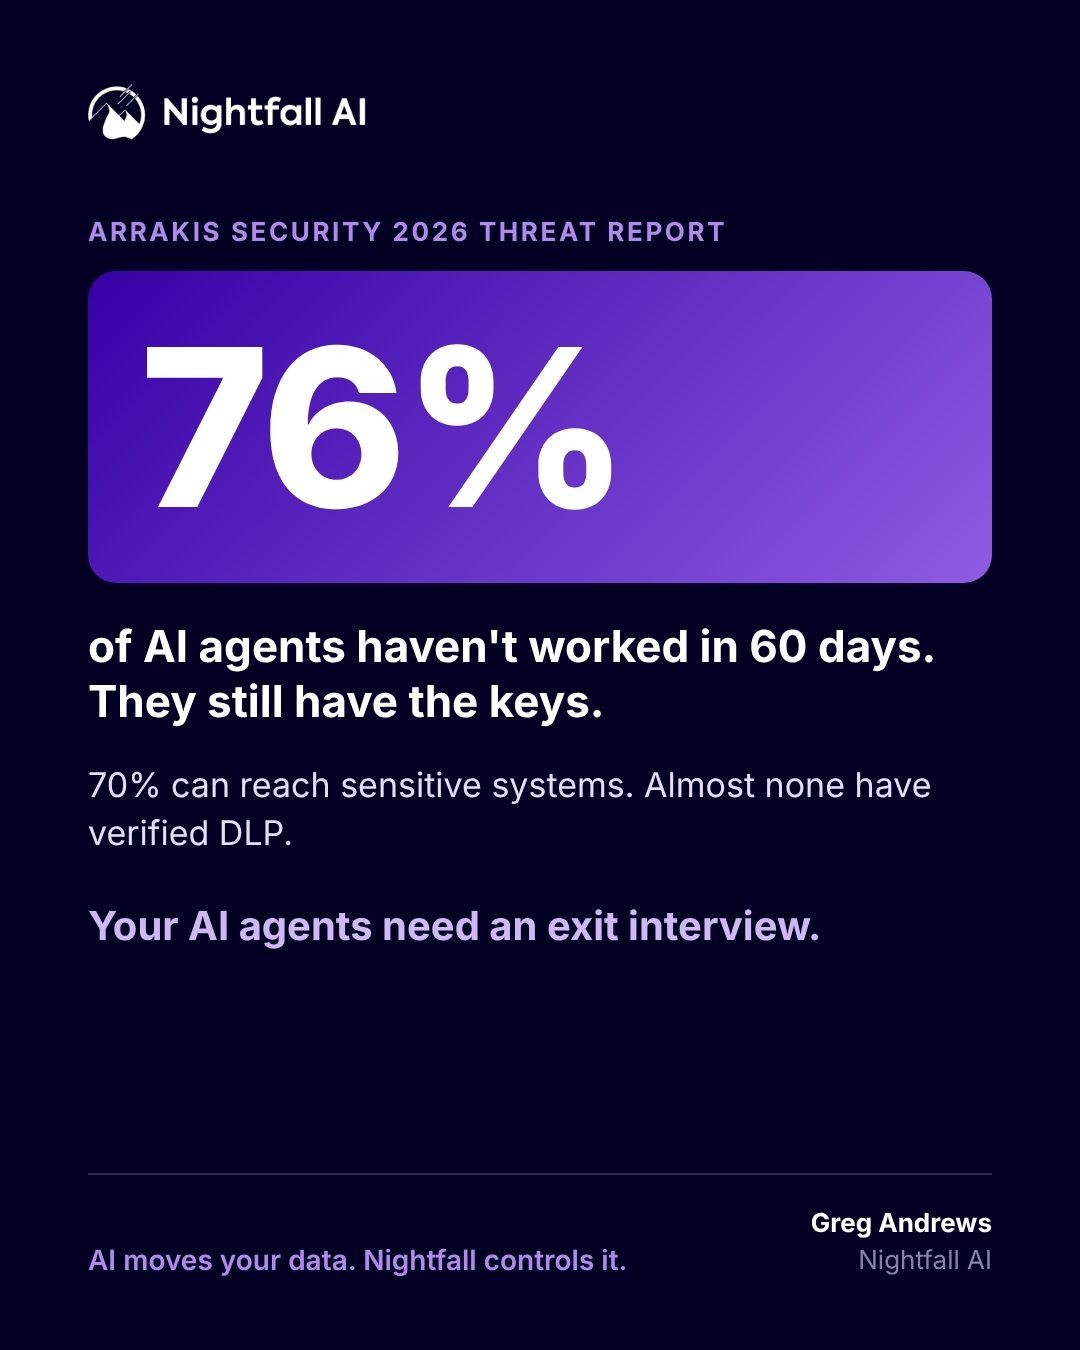
Most companies have AI agents that are basically former employees who still have a badge. A new Arrakis Security report found 76% of production AI agents haven't run in 60 days. Their credentials still work, and their triggers still fire. 70% can reach sensitive systems. Almost none of those connections have verified DLP. Somewhere there's an agent built for a spring project, still holding the keys to the data warehouse, waiting for someone to say its name. A quarter of the idle ones can be woken by an unsigned webhook from outside the company. Endpoint controls help with agents on laptops (Cyera and Bloom Security just teamed up on one). The forgotten agents tend to live in SaaS workflows and behind MCP servers. You'd cut off a departed employee's access the same day. Agents deserve the same exit interview. Nightfall AI controls what AI agents move in real time, whether anyone remembers them or not. Who offboards the AI agents at your company? #AIAgents #AISecurity #CISO #DLP
- LINKEDIN · IMAGESince 26 Oct 2026
My AI agent had a very productive morning. 9:01 AM: Pulled customer records from Salesforce. 9:02 AM: Queried the finance database "for context." 9:03 AM: Read a local file called final_FINAL_v7_DO_NOT_SHARE.xlsx. 9:04 AM: Called an MCP server nobody has ever heard of. 9:05 AM: Wrote a lovely summary and sent it somewhere outside policy. 9:06 AM: Security asks what happened. The agent never took a coffee break. It never asked permission. Honestly, it was the most productive employee we had this quarter. That's the issue. Legacy DLP was built for Dave from accounting emailing a spreadsheet to his Gmail. It was not built for an intern made of math that does 40 tool calls before your SIEM finishes loading. At Nightfall AI, we built for the new Dave: 🔹 MCP Gateway: approve the servers you need and block the rest by default. Your agent doesn't need to talk to "totally-legit-mcp-server-final2." 🔹 Inference Hooks: inspect and block prompts, tool calls, and responses inside the live Claude session, across web, desktop, Claude Code, Cowork, and Slack. 🔹 Nyx, our autonomous DLP analyst: triages what matters on day one, with no 6-month tuning project and no 400-line regex nobody understands. Live in one working hour. Not one fiscal year. One hour. AI is going to move your data either way. The only real question is whether you find out before it happens or in a postmortem. Agents work fast. Your security should too. #AISecurity #DLP #AgenticAI #MCP #CyberSecurity Andrew Snyder Angela D'Amico
- LINKEDIN · IMAGESince 20 Oct 2026
A file sync, a bulk download, a paste into ChatGPT. In the logs, routine work and data theft look the same. What separates them is intent, and intent doesn't show up in a volume score. Nightfall AI New User Risk Agents read the content, the context, who owns the data, and what happened right before. Then they give you a short list of cases worth your time instead of 10,000 alerts. It's like hiring a seasoned investigator who never needs coffee, never takes PTO, and never asks "can we circle back on this?" Join us live on Ocotber 21st at 200 pm: https://lnkd.in/enjN3FZy
- LINKEDIN · IMAGESince 19 Oct 2026
📅 LIVE THIS WEDNESDAY: PREVIEWING OUR USER RISK AGENTS Most insider risk investigations die the same way: a dozen alerts, zero narrative, and a week of pulling logs to answer "did this person actually take something?" We built User Risk Agents to do that work. They read the signals a human investigator would - who the user is, what the content is, where it went, and what happened before and after - then hand you a case file that holds up with Legal, HR, and your CISO. Join us Wednesday for a live preview: Building the Insider Risk Case. We'll walk through a real exfiltration scenario end to end: detection → investigation → case file. 📅 Wed, Oct 21 · 11:00 AM PT / 2:00 PM ET 🔗 REGISTER HERE: https://lnkd.in/gQcTNWw6 Can't attend? Register anyways, and we'll send over a recording. #InsiderRisk #DLP #DataSecurity #AIAgents
- LINKEDIN · IMAGESince 19 Oct 2026
Next Wednesday we’re going live on something that feels uncomfortably timely. 🟢 Oct 21, 11am PT: How Nightfall’s AI agents build the insider-risk case for you 🟢 This week OpenAI accused a former employee of walking out with 100+ files and taking it to Apple. However, insider theft quietly happens every day across companies all over the world: it’s a steady drip of ordinary-looking file moves nobody has time to look into. And the pattern is always the same. A sync. A download. Normal stuff, a few weeks before someone leaves. It only becomes a case once a human sits down and reads the content, the owner, the destination, and what happened right before. Most teams don’t have that human. So the real cases slip through. That’s the gap we built User Risk Agents for, now in early access. Two AI agents do the investigator’s work and hand you a case file instead of a pile of events. Come see it. Link in comments. #InsiderRisk #DataSecurity #AISecurity
- LINKEDIN · IMAGESince 15 Oct 2026
An OpenAI engineer allegedly copied more than 100 confidential files about an unreleased device to his personal accounts on his last day. Nobody noticed. It surfaced MONTHS later, in the middle of a legal investigation that had nothing to do with it. There was no breach to detect. No malware, no attacker. A person with normal access moved files he was allowed to open. That’s the gap most security teams still have. Legacy DLP was built to catch credit card numbers and SSNs. Ask it to recognize a hardware spec, a roadmap, a supplier list or a chunk of source code and it mostly shrugs. And the window when someone has given notice is exactly when that blind spot costs the most. Catching sensitive data is table stakes now. The harder problem is knowing what a file actually is, where it came from, who is moving it and where it’s headed, and blocking the transfer in the moment instead of reconstructing it in discovery four months later. That’s the problem we built Nightfall AI to solve. Worth asking your team this week: would your DLP have stopped this, or would you have read about it in a court filing? https://lnkd.in/gftrad-G #DLP #InsiderThreat #DataSecurity #CISO #Cybersecurity #OpenAI #Apple
6 of 229 adsSign up to see every Nightfall AI ad, filter by format and date, and get alerts on new ones.
See all 229 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.