On air · 1 of 3 networks
Maze
- mazehq.com
- GB
- 50 employees
Maze’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 361. Watch Maze with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 92 | Checked 29 Oct 2026 | See all 361 ads → | ||
| Meta | Not checked | — | |||
| Recently | 24 | Ads on the Google Ads Transparency Center | Checked 4 Oct 2026 | Collect them with the API → |
Maze has 92 live LinkedIn ads. We recorded 24 Google ads on 4 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 12 Oct 2026
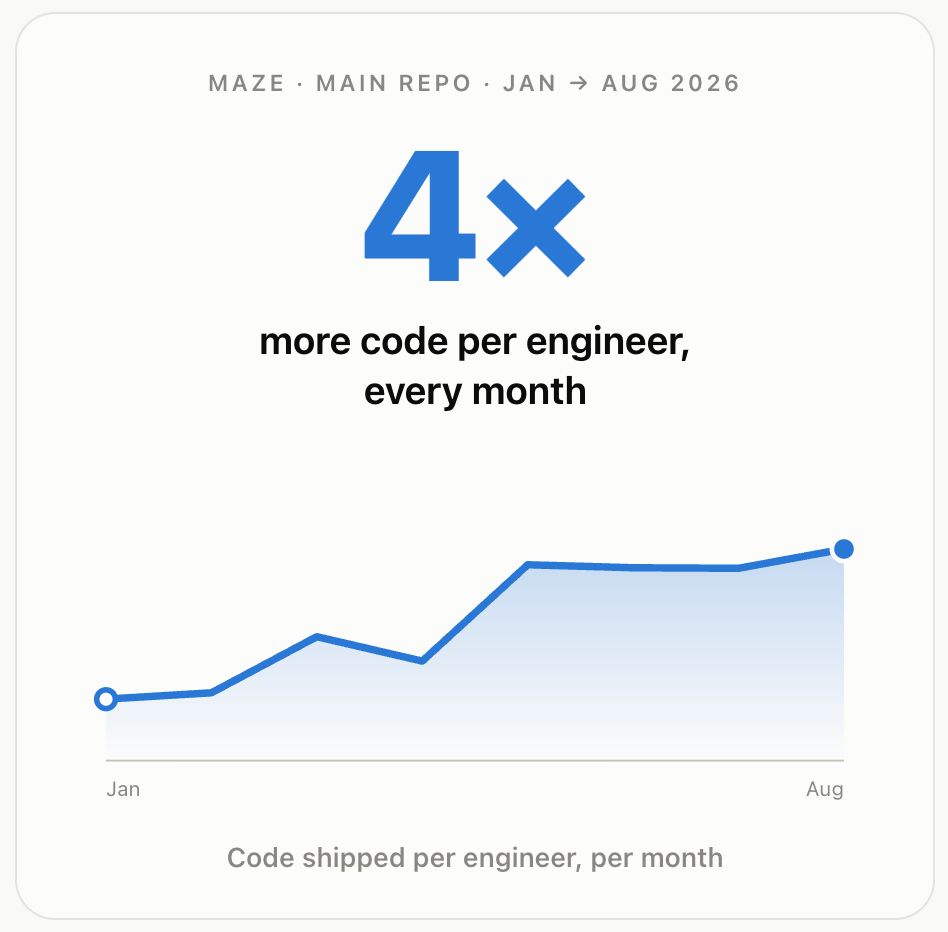
In seven months, the amount of code shipped per engineer at Maze increased by nearly 4x. The hardest part wasn’t technology or tooling, it was working with the team on a common approach. Some engineers worried they were being left behind as colleagues accomplished more with coding agents, while others could barely stop working. They had more ideas than ever, and suddenly each one was cheap enough to build and test. I'm convinced the human side is where most of the time goes, and it's the part that's easiest to underestimate when you're focused on the tooling. For us that meant sharing real workflows, talking honestly about what wasn't working, and pairing people who were at different stages of the transition. The improvement now shows up everywhere we look: code shipped, number of PRs, but also how fast features reach customers. Adopting coding agents is a group alignment problem. The day-to-day looks very different now, but we're still the ones deciding what to build and whether it's good enough.
- LINKEDIN · VIDEOSince 17 Sept 2026
Maze investigates every vulnerability in your environment, finds the ones that actually matter, and helps you fix them.
- LINKEDIN · IMAGESince 15 Sept 2026
Isn’t building AI products easy now? You can just plug in an API from Anthropic or OpenAI, build a few integrations, write a few prompts, and your product is good to go? You just lean on the intelligence of the models to carry out whatever agentic task you need? This might be true for some use cases, but what if your use case: - needs agents to run millions of times every day - with ~0% tolerance for incorrect results / hallucinations - and, if you fail, your customers suffer cyber breaches That’s what we have to deal with at Maze. For a single customer, we have to investiagte millions of potential vulnerabilities across tens of thousands of assets every day. That’s 100s of millions of potential investigations, all handled with AI agents, with almost zero tolerance for mistakes. Given such hard constraints we’ve had to tackle so many challenges to make the product as accurate and cost efficient as it is today. What’s been fascinating is that given enough time and smart people, there is so much engineering you can do around the models to solve seemingly impossible problems. We haven’t figured it all out yet, but I’d hope to say that a lot of the things we’ve done can help people inside and outside of security building with agents. No one is better to learn from on this topic than Santiago Castiñeira. He’s doing a session soon sharing some of what we’ve learnt, you can sign up here! https://lnkd.in/et6Gd2Ja
- LINKEDIN · IMAGESince 15 Sept 2026
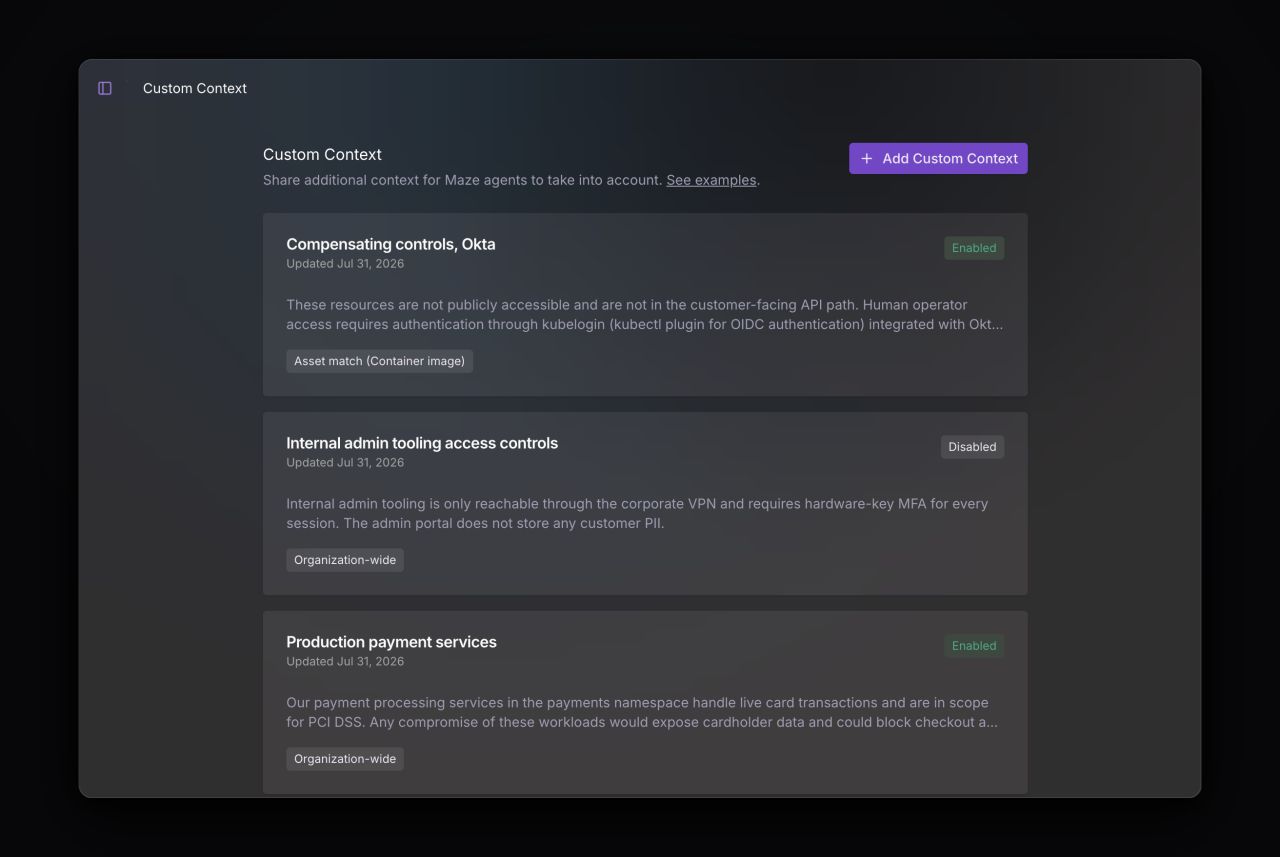
Something interesting we built at Maze recently... How many times over the years have you heard about security products struggling to understand business context? Flagging 10 findings equally because they're all technically a risk, even though only one could do any real harm to the business? A lot of attempts have been made at solving this but before AI often the best we could do was manually labelling important assets as 'crown jewels'. Or, we could build CMDBs to track assets and gather context about them but a) it was still difficult for security tools to pull in and use this context b) approximately 100% of the people I've met who've built a CDMB say that it's so out of date it's practically useless 😂 Now that we're building security tools with AI rather than rule-based logic, all of this should change. If a security product is using AI agents to make its decisions, you should be able to upload or connect practically any document or unstructured form of business context, and the AI should understand what it is and be able to reference it in it's analysis. We recently built something that does exactly this. You can now upload any unstructured content you like into Maze and our agents will automatically understand what it means. Then, whenever they investigate vulnerabilities, they factor the new context into their analysis, meaning they can be even more accurate in finding the stuff that matters. It seems likely that over the next few years, as security products become AI-based, we can start to integrate more and more sources of business context. We should be soon b able to stop complaining about security tools not understanding the business. And, even better, we might be able to stop pretending to use our CMDB...
- LINKEDIN · EVENTSince 10 Sept 2026
- LINKEDIN · IMAGESince 9 Sept 2026
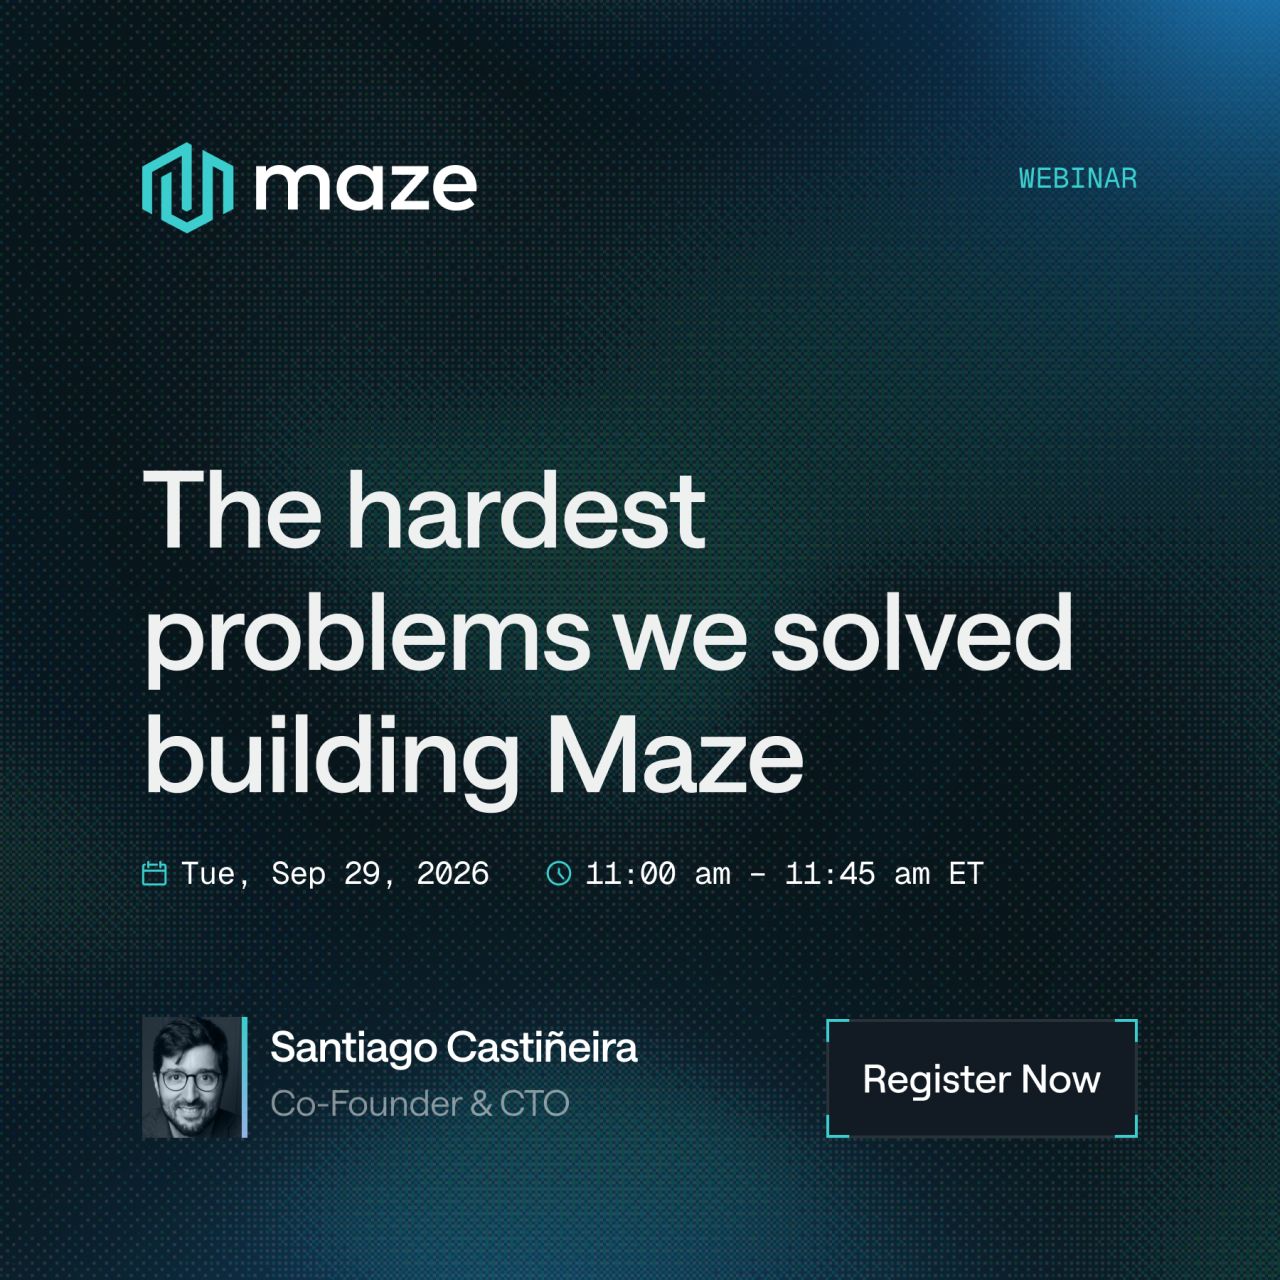
When we started building Maze, I knew it would be hard. Some problems still caught us off guard. On Tuesday, September 29 at 11:00 AM ET I'll walk you through some of the toughest challenges we found between a working MVP and successfully investigating millions of vulnerabilities weekly. Come with questions and skepticism. Register here --> https://lnkd.in/eJQjvgaW
6 of 361 adsSign up to see every Maze ad, filter by format and date, and get alerts on new ones.
See all 361 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.