On air · 1 of 3 networks
Lema AI
- lema.ai
- US
- 53 employees
Lema AI’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 554. Watch Lema AI with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 554 | Checked 29 Oct 2026 | See all 554 ads → | ||
| Meta | Not checked | — | |||
| Recently | 3 | Ads on the Google Ads Transparency Center | Checked 3 Oct 2026 | Collect them with the API → |
Lema AI has 554 live LinkedIn ads. We recorded 3 Google ads on 3 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 27 Oct 2026
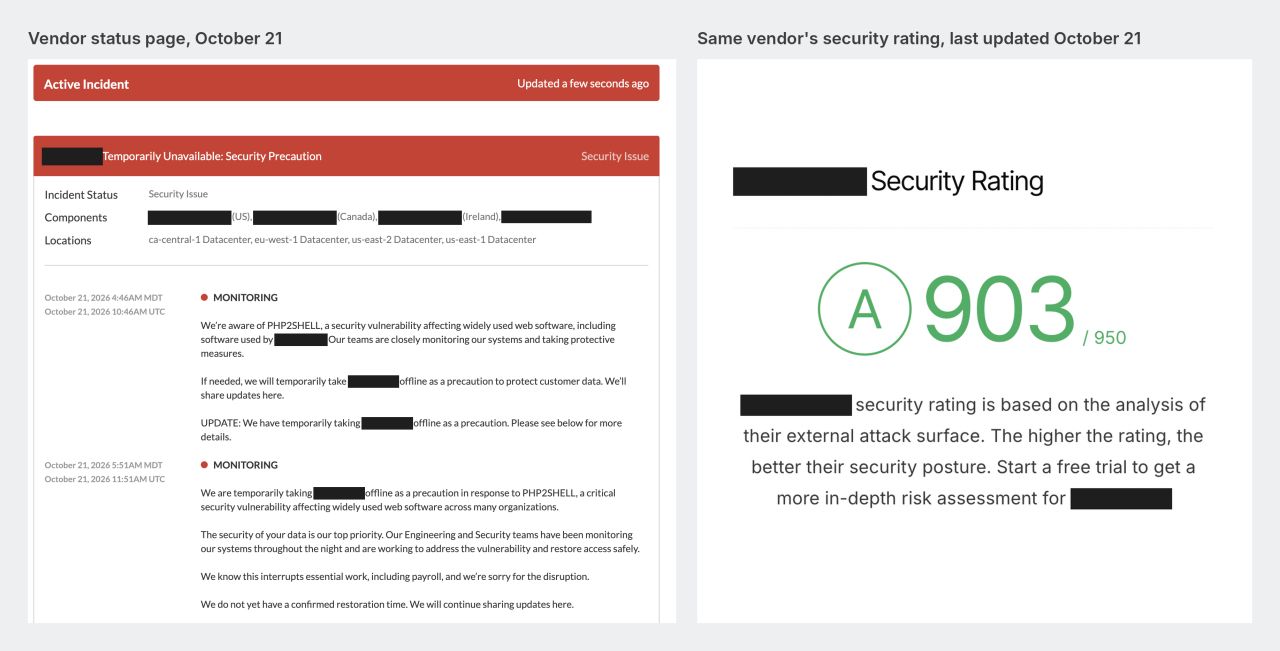
Yesterday, a major HR and payroll platform went offline while responding to PHP2Shell. We were affected too. Its security rating that same day? A. 903 out of 950. And I don't think the rating was wrong. It measured what it was built to measure: the vendor's externally visible security posture. But we've gotten used to treating a vendor's security score as a measure of how much risk that vendor poses to us. Those aren't the same thing. The vendor going offline doesn't mean it has bad security. Taking systems down may have been exactly the right security decision. But if your payroll depends on that vendor, the impact on your business is real regardless of how good its security is. We spend so much time evaluating how secure our vendors are, and far less understanding what happens to us when something goes wrong. That's what we're building at Lema. We connect what's happening at the vendor to the data, access, and business operations that depend on it, so security teams can see where they're actually exposed and what they can do about it. See how Lema works: https://lnkd.in/eauWSdZe
- LINKEDIN · IMAGERecorded 27 Oct 2026
Imagine paying for a SOC 2 audit and getting a report identical to the other 500 companies. That’s what a YC-backed compliance startup got caught doing: issuing literal copies to its customers. Nearly identical language, no exceptions. Hundreds of companies had already accepted them as proof their vendors were secure. That's not an edge case. That's what most TPRM programs actually run on: vendor-supplied evidence, reviewed once and filed. Nobody checks it against what the vendor can actually reach inside your environment. I go deeper into why current TPRM programs don't actually reduce risk here: https://lnkd.in/dhpRT5Pd
- LINKEDIN · IMAGERecorded 27 Oct 2026
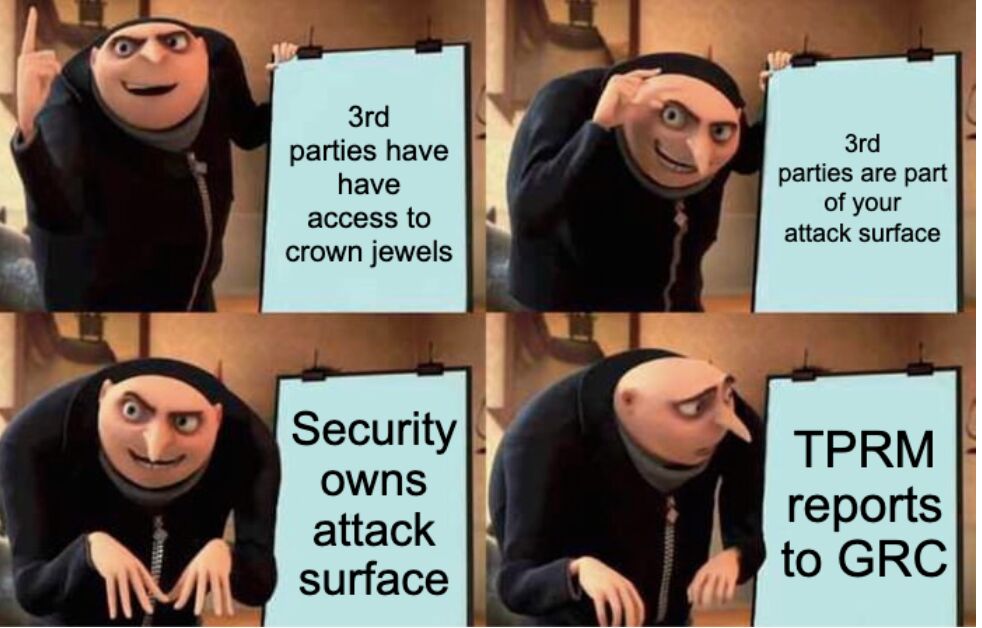
Hot take: TPRM should be under security, not GRC. Your 3rd parties have access to your systems and your data. That makes them part of your attack surface, same as a server or an endpoint, except you didn't build it and can't patch it. Security owns every other asset. 3rd parties are the one glaring exception, and it's mostly an accident of history. TPRM grew up as a banking compliance obligation, back when cyber was one line on a long risk list. To be clear, I'm not saying move the whole function. Whether a vendor is financially stable, concentration, contracts, insurance, leave that with GRC and legal. I'm talking about the security piece. And security doesn't do it alone either. It still needs what the traditional TPRM team knows. What got scoped and approved in the first place, which of a vendor's products are supposed to be in use. That context is the input, but managing the exposure is security's job. If it behaves like attack surface, put it with the team that deals with attack surface. This is exactly what we built Lema for - giving security the tooling to own the third-party attack surface. Book a demo: https://lnkd.in/eiKrm9DC
- LINKEDIN · IMAGERecorded 27 Oct 2026
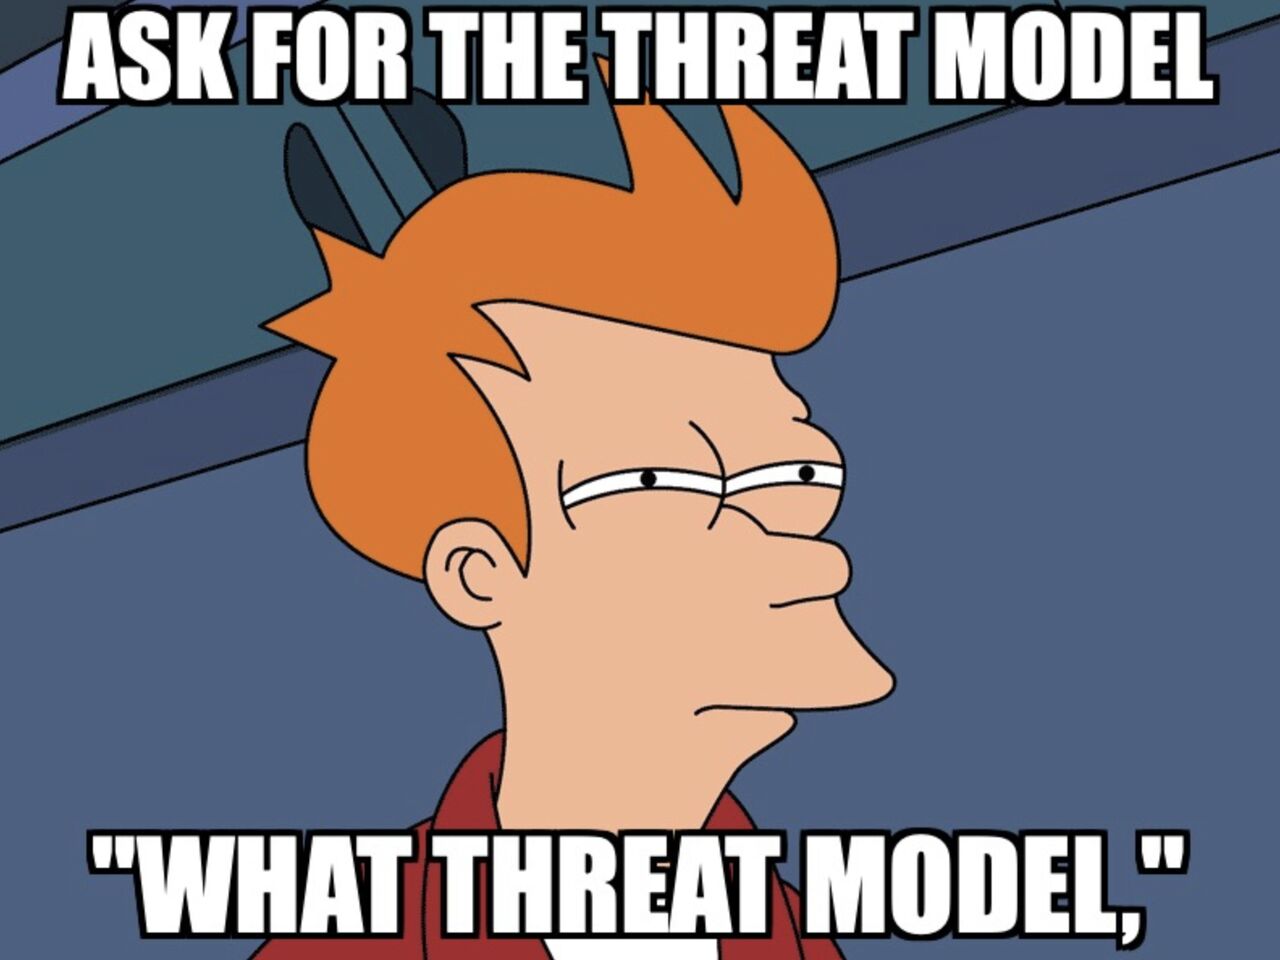
Prove that a breach in your environment does not become a breach in ours. That's what you should ask every vendor before you onboard them. It's not in a SOC 2. It's not on your questionnaire. So ask it out loud and see what comes back. Ask for the threat model. If the answer is "what threat model," you already have your answer. Lema maps what each vendor can actually reach in your environment, and every finding ships with a fix to reduce your exposure. Book a demo: https://lnkd.in/ezdJAhVD
- LINKEDIN · IMAGERecorded 27 Oct 2026
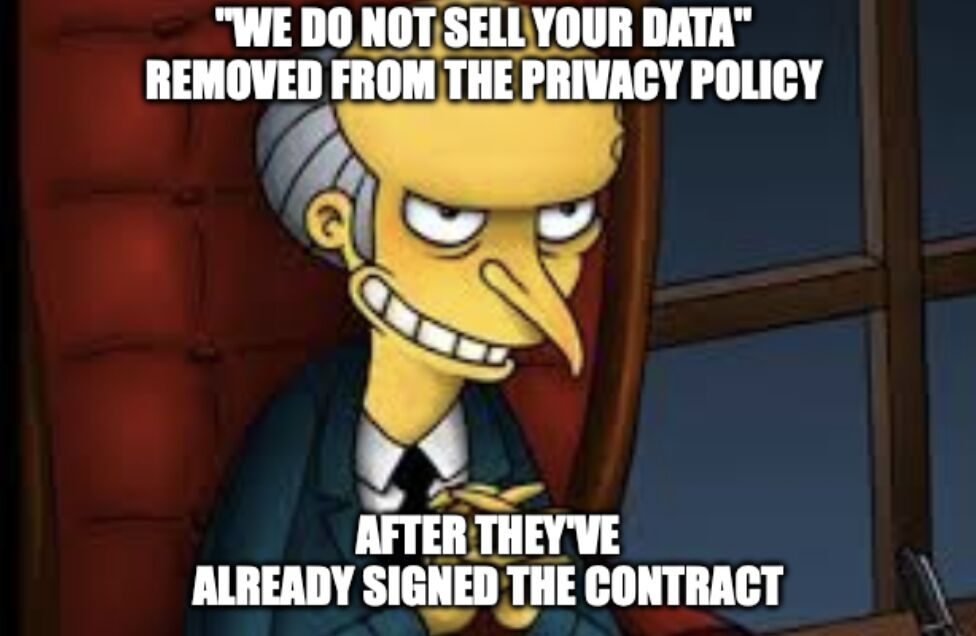
A company got hit with a class action for training its AI on recorded customer calls without proper consent. A week after the suit became public, it quietly updated its privacy policy: naming itself the "controller" of that data for AI training purposes, with an opt out routed to an inbox that nobody reads. A separate vendor made the same move after a different lawsuit, this one over selling customer data. The line that used to read "we do not sell your data" simply disappeared from the policy. No announcement, no changelog, no email to existing customers. Vendors don't put bad news in a press release. They put it in paragraph fourteen of a privacy policy update, on a date nobody's watching. If you only reread a vendor's policy at renewal, you're finding out a year late. Lema reads those policies when they change, and flags the ones that impact your exposure. Book a demo to see what it looks like: https://lnkd.in/eTrfxhx7
- LINKEDIN · IMAGERecorded 27 Oct 2026
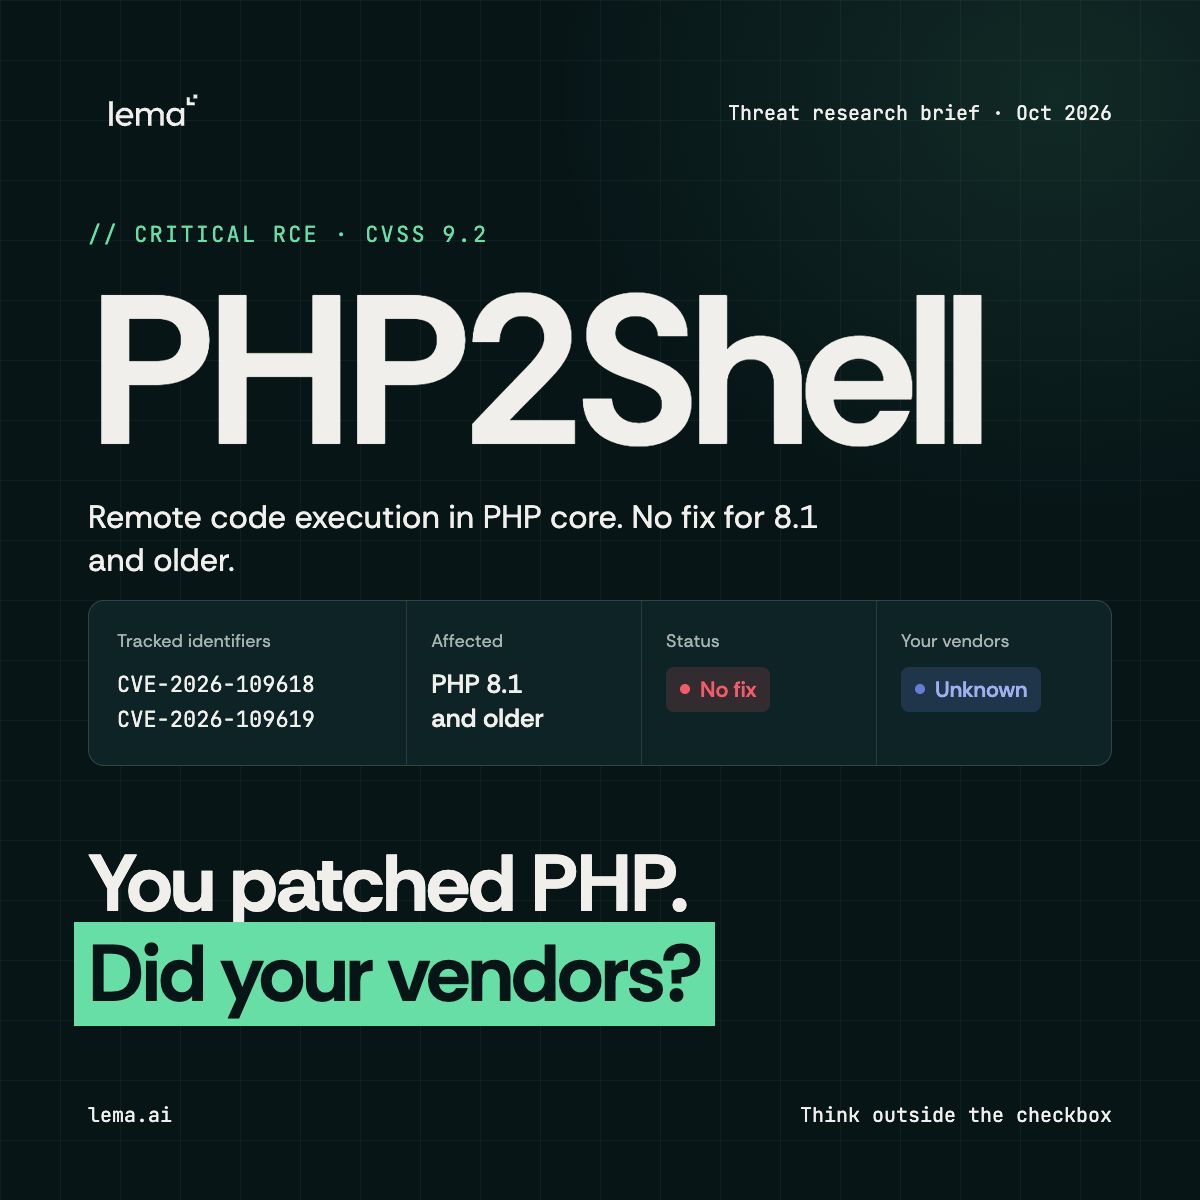
🚨 Two critical PHP flaws, nicknamed PHP2Shell, leaked yesterday ahead of an emergency patch. PHP’s security team rates both 9.2 on CVSS v4.0. Fixes only cover supported branches 8.2 through 8.5, so anything older gets no patch at all. That’s a big group. Mallory counted about 884,000 internet-facing hosts with a PHP 8.1 or older banner. Most security teams are scanning their own perimeter right now. That’s the easy half. Your real attack surface is your own plus every vendor’s, including the shadow vendors nobody formally onboarded. You can’t patch their servers, and you probably don’t know which of them run PHP. Lema has already started active scans across hundreds of thousands of our customers’ vendors to find exposed PHP before attackers do. You could have hundreds of vendors running vulnerable PHP. You can't contact all of them at once, and not all of them pose the same risk to your organization. So who do you go after first? We broke down how to prioritize vendor outreach for PHP2Shell, what to ask, and how to handle vendors that can't patch immediately. Read the post: https://lnkd.in/en6CpsD2
6 of 554 adsSign up to see every Lema AI ad, filter by format and date, and get alerts on new ones.
See all 554 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.